
Search
Merge
Play Audio Prompt
DTMF
Disconnect
The basics
Shift Synchronization
Power Frame
Create App Registration for Attendant Console
Callback request
Force terminate
Supervisor Assist
Redirect
Virtual wait
Conference call
Outbound DTMF
Cancel consultative transfer
Call Park
Features
Smart Chatbot
Microsoft Power Automate
Phonebook
Sentiment Analytics
TouchPoint
Agent
Reporting
Supervisor
Agent
Obtaining a WhatsApp number
What to do next?
Signup & Enrollment
Summary Export
ReplicatorConfig
ReplicatorJobStatus
TouchPoints
Chatbot Languages
Chatbot Knowledgebases
Tenant Information
Subscription
Conversation Packs
Conversations
Messages
Toastar Users
Toastar Conversations
Teams
WhatsAppConsent
API TouchPoint
Campaign API
Transcript
FeedbackExport
Outbound Call Campaign
Webhooks
Agent EventLog
Agent workEntry
Call Stream Change
Execution Results
Request
Queues
Calls
Agent Export
CallParticipants
API Documentation
ToastarForTeams
Callback Requests
Conversation API
Classification API
General Prerequisites
Access Control
Call Park
Api Keys
Email
Contact Center
Setup Access & Security
Schedules
Resource Accounts
Queues
Callflows
Audio Files
Agents
Logging
Audit
CRM
Languages
Create Tenant App
Getting started
Subscriptions
Call Flows
AI Flow
Copilot Touchpoint
Insights & Analytics
Wallboard
Permissions
Logging
CRM Calling Integration (Toastar)
Custom CRM Connector
Default CRM Connectors
CRM Replicator
Email Configuration
Schedules
Agent Assist
Setup Access & Security
Malicious File Blocking
Wallboard
Reporting
Messages
Examples
Graphical Designer
Using the library
Email Touchpoint
API TouchPoint
Facebook TouchPoint
SMS TouchPoint
WhatsApp for Business TouchPoint
Webchat TouchPoint
Microsoft Teams
Queues
AI Flow (Beta)
Classification
Skill Based Routing
Reason Codes
Audio Prompts
Agent Profiles
Agents
Call Park
Resource Accounts
Graphical Designer
Form Based callflow
Using the library
Queues
General
Agent page functionalities
Social Messaging
Contact Center
Support & Assistance
Compliance by design
Social Messaging
Contact Center
Getting Started
General
No results
Try a different search query
Access Control
Access Control limits which items a user can see and manage in the portal. It lets several organisations (in this example: two companies) share one Azure tenant and one portal, while each administrator only sees and manages their own company’s items.
Example setup
- One Azure tenant with two companies: Company 1 and Company 2.
- Company 1 admin has the Entra role UnifAI-Admin. This is a super admin who can configure everything, including security features.
- Company 2 admin has the Entra role UnifAI-Portal user. This role has no access to the security features like Access Control, Audit, API keys, Logging and General settings. This admin only works with items in Company 2.
Building blocks
1. General settings
This is only setable for the user with the UnifAI-Admin role.
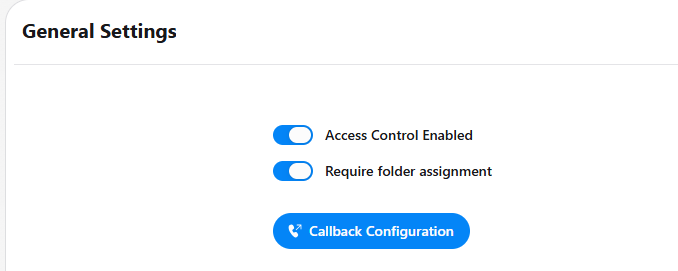
- Access Control Enabled turns the ACL feature on or off for the whole installation.
- Require folder assignment controls whether items must belong to a region:
- Off: items such as prompts, queues and resource accounts can be created without a region. If no region is selected in the region picker, they are saved under Unassigned Items.
- On: creating unassigned items is not possible. Every new item must be placed in a region. This is the recommended setting for a two-company installation, so that no item ends up outside a company.
2. Access Control → Permissions
This page has three tabs.
Regions
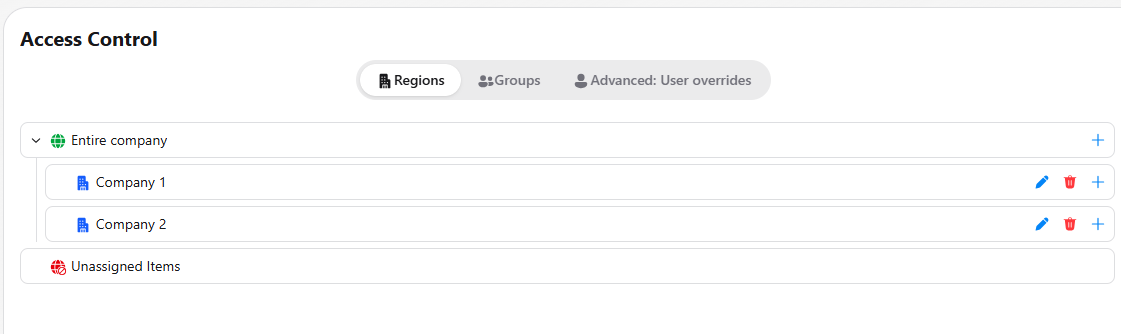
- Shows the region tree: Entire company at the top, with Company 1 and Company 2 below it, plus the special node Unassigned Items.
- Regions can be added (+), renamed (pencil) and deleted (bin).
- When you create a child region, it copies the permissions of its parent. After that, each region has its own rules. Regions do not inherit from their parent.
Groups
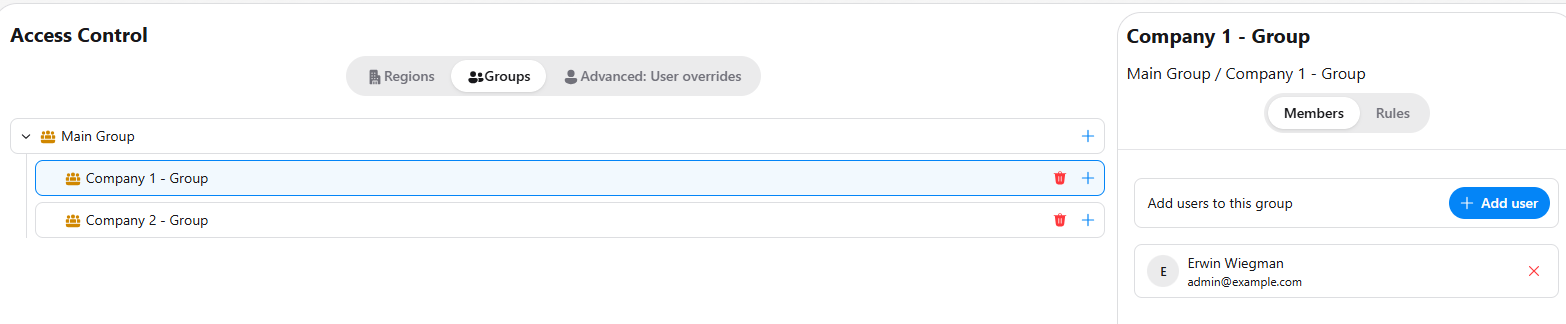
- Shows the group tree (Main Group → Company 1 - Group / Company 2 - Group).
- Each group has two sub-tabs:
- Members: the users in the group (+ Add user).
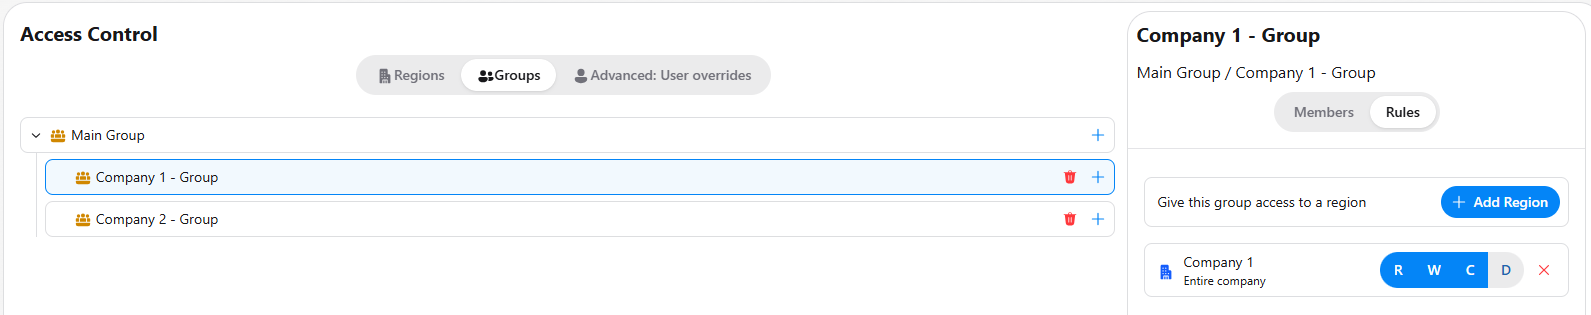
- Rules: the regions the group may access (+ Add Region), each with its own R / W / C / D toggles.
- Group rules are inherited down the group tree.
- The admin who configures the rules decides the rights per group. In our example, Company 1 - Group has R, W and C on Company 1 but not D. Its members can see, change and create items, but not delete them.
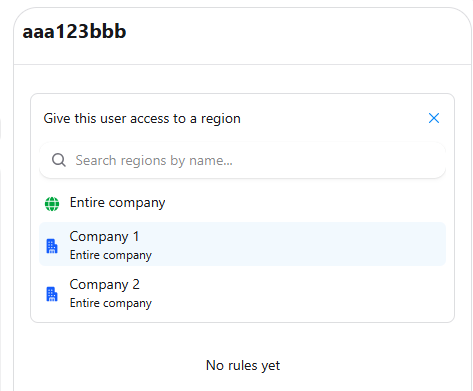
Advanced: User overrides
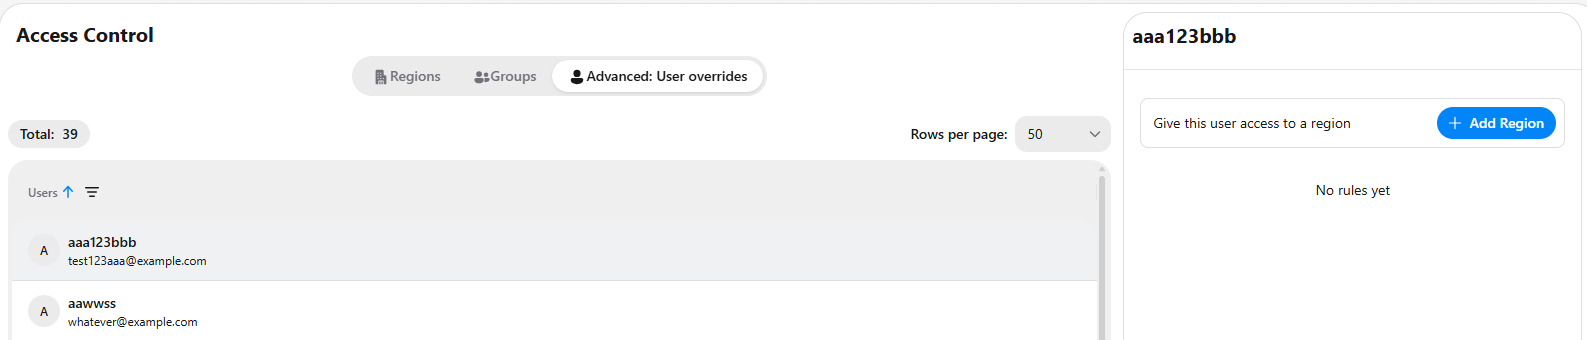
- Shows all users, with a search/filter.
- For a selected user, you add a region directly and set that user’s rights (R / W / C / D) for it. These rights apply to that user instead of the rights from a group. Use this for exceptions that do not fit a group.
3. Access Control → Assign items
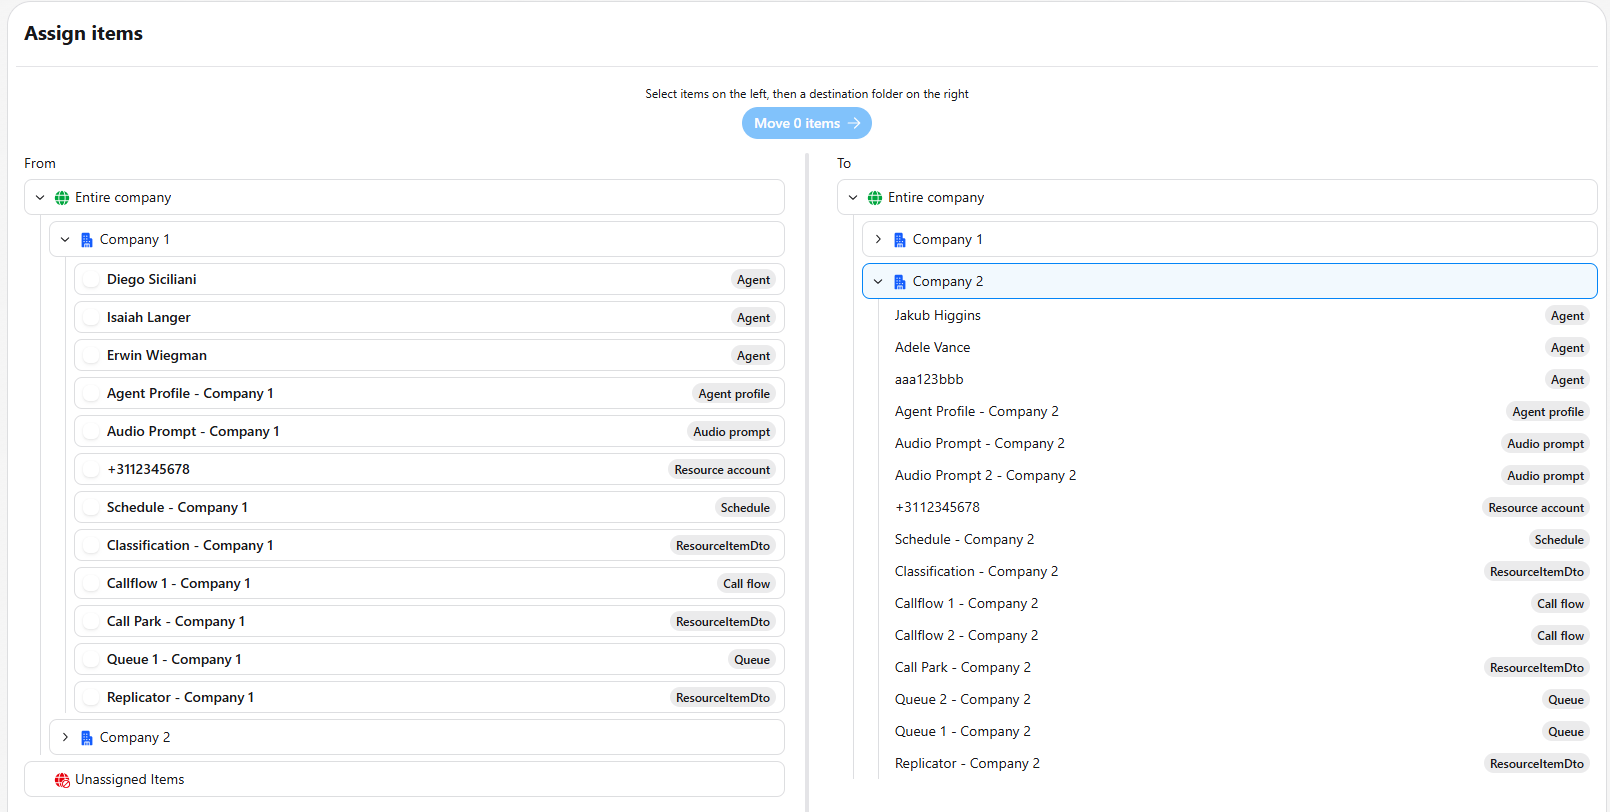
- A two-pane screen: From (left) and To (right).
- Select one or more items on the left, select a destination region on the right, and click Move x items.
- This is how existing or unassigned items are placed in Company 1 or Company 2, or moved between them.
4. Region picker (top right)
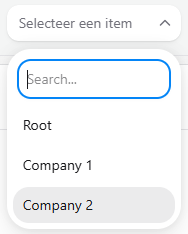
- A dropdown at the top right of the portal, listing Root (= Entire company), Company 1 and Company 2.
- It sets the active region. When a user creates a new item (prompt, queue, resource account and so on), the item is saved in the selected region.
- If no region is selected and Require folder assignment is off, the item is saved under Unassigned Items.
Example scenario
- The Company 1 admin (UnifAI-Admin) enables Access Control and Require folder assignment.
- The admin builds the regions Company 1 and Company 2, and moves existing items to the right region using Assign items.
- The admin creates Company 1 - Group and Company 2 - Group, adds the right users as members, and gives each group rules on its own region only (for example R, W and C, but no D).
- The Company 2 admin (UnifAI-Portal user) logs in. The security menus (Access Control, Audit, API keys, Logging, General settings) are not available. Only the items in region Company 2 are visible, so this admin works in a filtered view. New items are saved in Company 2.
- The Company 1 admin can see and configure everything across both companies, including the rules that apply to the Company 2 admin.